As a founder myself, I know how easy it is to assume state espionage only happens to defence primes and government departments.
It doesn’t. If your company holds valuable intellectual property, early-stage research or sensitive data, it may already interest a hostile state. You are also likely to be easier to reach than the big players. That is the problem the UK’s new Secure Innovation Security Review is designed to address. As one of the scheme’s Approved Reviewers, I want to explain what it is, who it is for and why I think it matters.
Why early-stage tech is an attractive target
Certain states deliberately target emerging technologies to fast-track their own economic and military capability. Taking a design, a dataset or a team’s know-how is quicker and cheaper than developing it from scratch.
Start-ups are attractive for simple reasons. Security is rarely anyone’s full-time job. Investors, partners and new hires arrive quickly, often before anyone has asked who they really are. And the most valuable information often sits on a handful of laptops.
None of this is negligence. It is what growth looks like. But it can leave a wide gap between the value of what a company holds and the protection around it, and anyone weighing up targets will notice that gap.
What is the Secure Innovation Security Review?
NPSA and NCSC, the UK’s national technical authorities for protective and cyber security, developed the Secure Innovation campaign. The Security Review scheme builds on it by giving early-stage technology companies part-funded access to an Approved Reviewer. Innovate UK administers the scheme.
The first year supported over 200 companies. The next round is now open, with the aim of reaching up to 1,000 organisations over the life of the scheme.
Each Secure Innovation Security Review includes:
an in-person review of your current protective security
a confidential, tailored report with practical recommendations
a £300 Cyber Essentials voucher
a follow-up session six months later to check progress
The review is valued at £3,000. Your company contributes £500, including VAT, and government funds the rest.
More than a cyber check
It’s easy to hear “security review” and think of firewalls and passwords. Cyber security is part of it. But a Secure Innovation Security Review looks at the wider picture: governance, security culture, risk management, supply chains and partnerships, incident management, and physical and personnel security.
That breadth matters. A determined adversary does not limit itself to one route in. It might use a phishing email, a well-placed job applicant, an overly curious investor or an unlocked lab, whichever is easiest. A review that only examines one of those routes leaves the others open.
I approach every assessment with three questions. What are you protecting? What are you protecting it from? How vulnerable is it? For a young tech company, the honest answer to the first question is often bigger than the founders expect, which is exactly why the other two matter.
Who can apply?
To qualify, your company must:
be registered and based in the UK
have fewer than 250 people
work in one of the 17 sensitive areas of the economy set out under the National Security and Investment Act, or in selected sectors from the UK’s industrial strategy
be willing to commit time, and potentially budget, to improving its security, including the six-month follow-up
Funding is limited and goes to eligible companies on a first-come, first-served basis, so it is worth applying early.
It is also worth being clear about what the scheme is not. It is not a certification, and there is no badge at the end. What you get is an honest, expert view of where you stand and a practical plan to improve it. You can still tell customers and investors that you have completed a review, and that is a conversation worth being able to have.
Choosing your reviewer
When you apply for a Secure Innovation Security Review, you can read the profiles of the Approved Reviewers and choose who you would like to work with.
I’ve spent the last ten years building my own technology company, so I understand what you’re going through: limited time, tight budgets and a long list of priorities competing for both. Security is my business, but I understand why it can slip down yours, and I don’t judge that.
That founder’s view sits alongside the professional one. I’m a Chartered Security Professional, with a background spanning military service, law enforcement and over two decades of senior security consulting. My aim is simple: you leave knowing what matters now, what can wait, and what to do next.
If that sounds like the right fit, look for Paul Mercer on the list.
A generic threat picture tells you what is out there. It cannot tell you who wants to disrupt this organisation, this site, this project or this event, whether they intend to, and whether they could.
The question I have been working on is whether the structured legwork behind that judgement can be done far faster, while leaving the judgement itself with the analyst. This article walks through one assessment from start to finish, including how the analyst and the system work through the findings together.
The worked example: a Christmas market in Leeds
I needed a subject I could publish without exposing anyone’s real threat profile. So I invented one: the Leeds Millennium Winter Market 2026, run by a fictitious operator, Northlight Events Ltd, in Millennium Square from 13 November to 23 December.
The market has around 90 timber chalets, a 600-seat beer hall and a stage, with up to 5,000 people on site at peak. I invented the market and its operator, but the location, the sources and the crime data are all real.
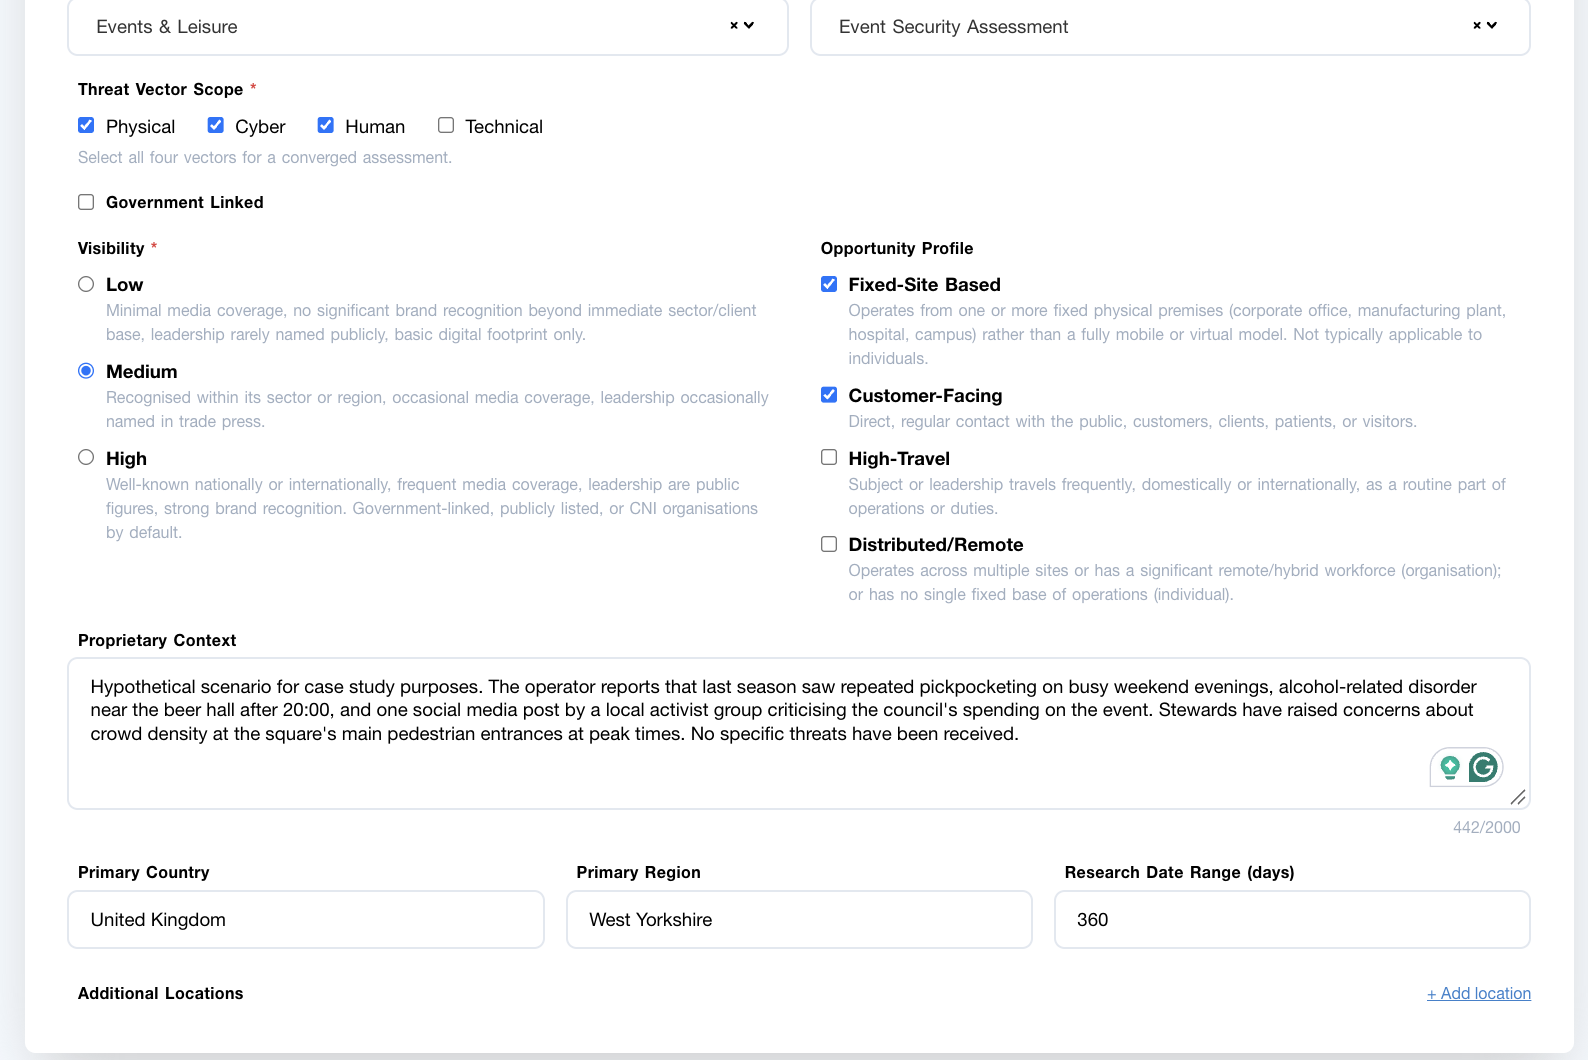
The assessment starts with the analyst defining the subject, and this is the first place the human sets the guardrails. I chose the threat vectors in scope (physical, cyber and human). Technical threats stayed out, because counter-eavesdropping is not a concern for a Christmas market. I rated its visibility as Medium against the system’s own definitions, as a regional event with local media coverage.
I also added proprietary context, the kind of insight public sources cannot provide: pickpocketing on busy weekend evenings last season, alcohol-related disorder near the beer hall after 20:00, a critical social media post by a local activist group, and stewards’ concerns about crowding at the main entrances.
Defining the subject. The analyst sets the scope, the visibility and the proprietary context before any research begins.
You can’t protect what you don’t understand
Before it looks at a single threat, the system builds the context: the venue, the operator, the surrounding area and the regulatory environment the event operates under. It did this in under five minutes. Done properly by hand, I would expect that to take an experienced analyst at least a couple of hours.
Most of it was right. It placed the square correctly in Leeds’s civic quarter, alongside the Civic Hall, Town Hall and City Museum. It also picked up its standing capacity of around 6,000, and worked through licensing and payment card obligations.
What it had not done was look at the most obvious precedent. So I asked it to research attacks on Christmas markets across Europe over the last decade. It came back with the cases any practitioner would expect, Berlin in 2016, Strasbourg in 2018 and Magdeburg in December 2024, where six people were killed and more than 300 injured. I checked each one against its source before accepting it.
That exchange set the pattern for the rest of the assessment. Time spent verifying the context is never wasted, because every threat that follows is built on it. Anything left unchecked there carries into the threat analysis, the narrative and, eventually, the risk picture.
Only when I was satisfied did I confirm and lock the context.
The threat picture in under five minutes
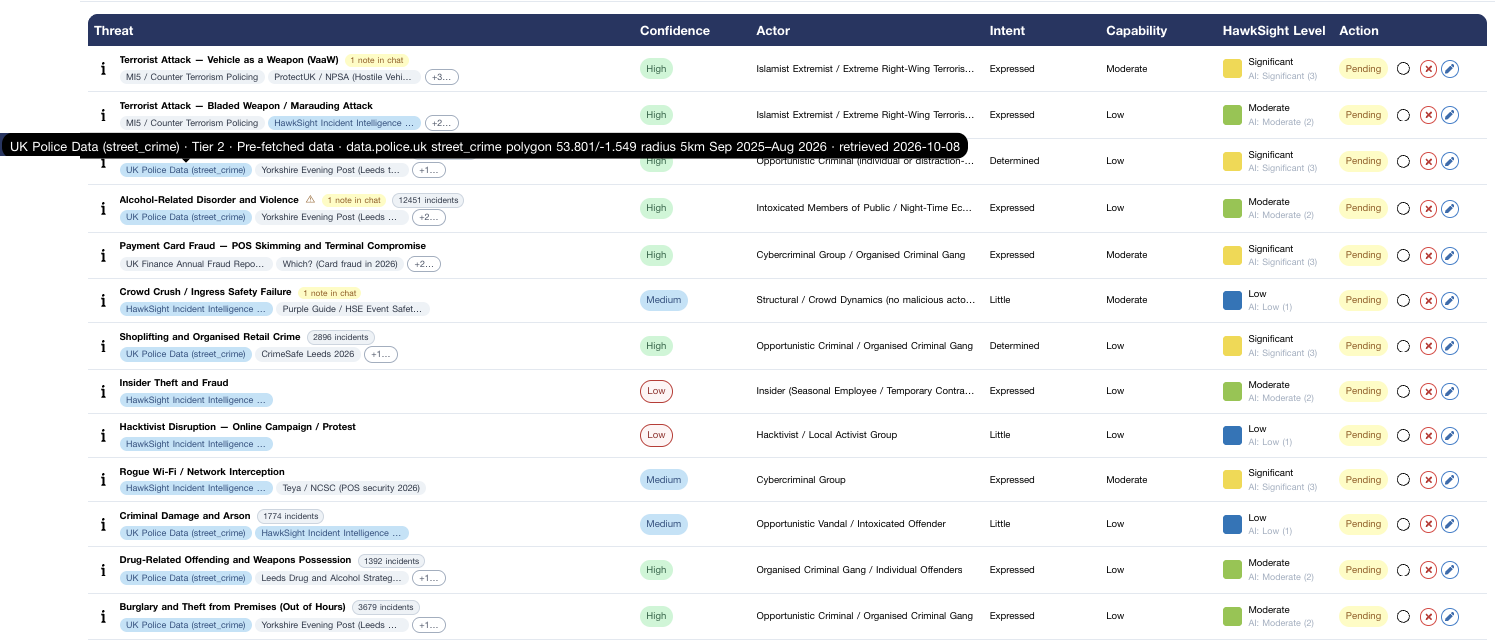
With the context locked, Talon identified 13 threats in under five minutes. My own estimate for doing the same work by hand is two to three hours.
For each threat it names the likely actor, assesses their intent and capability, rates its confidence and cites every source it relied on. Its suggested threat level sits beside the analyst’s own. You can see at a glance where you have agreed and where you have overruled it.
The research draws on a controlled set of sources rather than the open internet: an aggregation of more than 750 news and intelligence sources in multiple languages, government advisories such as MI5 and Counter Terrorism Policing, sector sources such as UK Finance and the NCSC, and official police data. Analysts can tailor the source set to what their own work relies on.
The threat table. Hovering over a source shows exactly what was retrieved: here, UK Police Data for a 5 km radius around the site, September 2025 to August 2026.
Official police data, down to the individual record
The biggest improvement since my first test run is the police data. Talon now draws recorded crime for the area straight from data.police.uk. Within 5 km of the square, that came to 61,010 recorded offences over 12 months, including 805 thefts from the person.
A 5 km radius takes in most of central Leeds, so that is a baseline for the city centre rather than a picture of the square itself. The system said so itself, noting that the concentration on busy weekend evenings during the market season would be considerably higher.
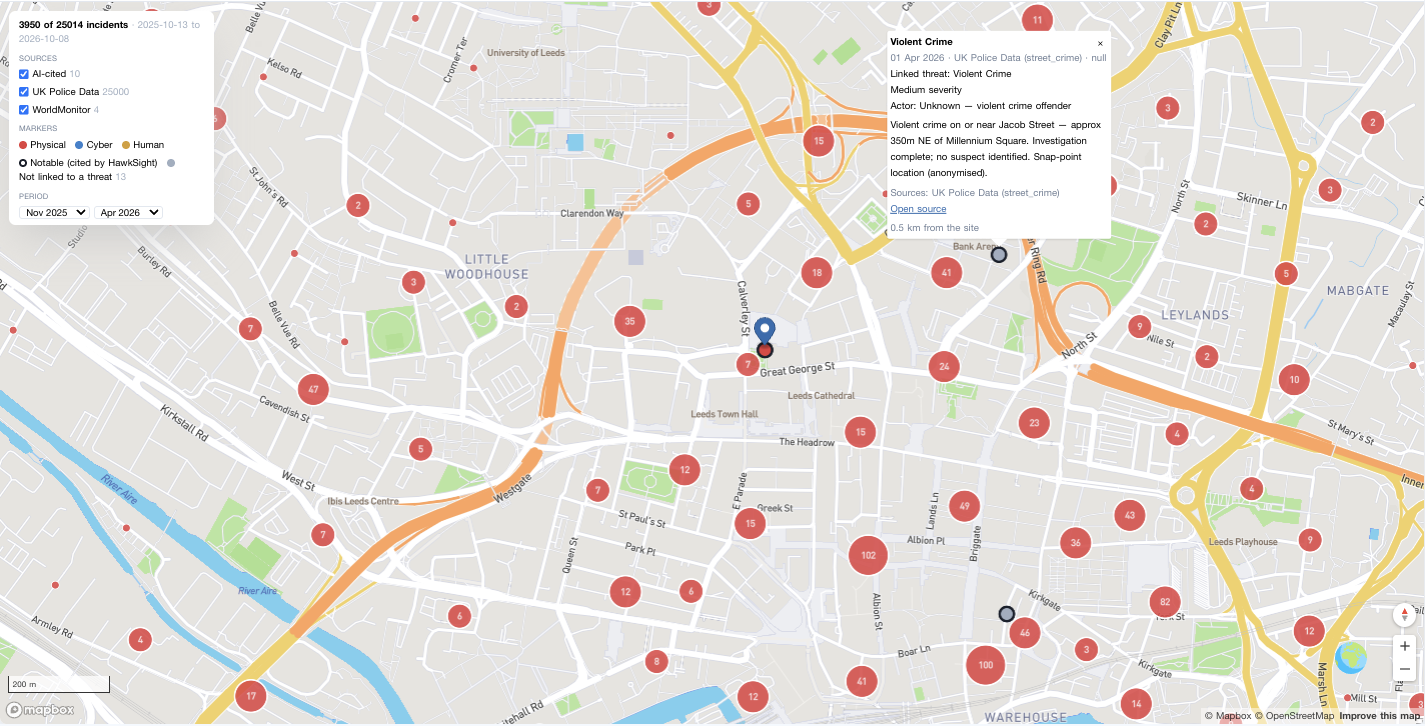
Every point on the map traces back to an official record. Open one and you see the offence, the month, the outcome and a link to the source.
Twelve months of police-recorded crime around Millennium Square, with a single record open: a violent crime in April 2026 near Jacob Street, about 350 m from the square. Investigation complete, no suspect identified.
Two other details stood out. The system tagged one threat, crowd crush at the entrances, as having no hostile actor at all. That is a safety risk rather than an adversarial one. I am genuinely interested in whether others would keep it in a threat assessment.
The system was also candid about its limits. It rated its overall confidence as Medium-High and explained why its cyber findings were only Medium. It also listed the sources it could not reach, from conflict event data with nothing inside the radius to event licence conditions that are not published.
Adversarial threat assessment: the analyst and the machine
This is the part of the exercise I most wanted to show. Every output is a draft until the analyst has verified it, and the system is built to be questioned.
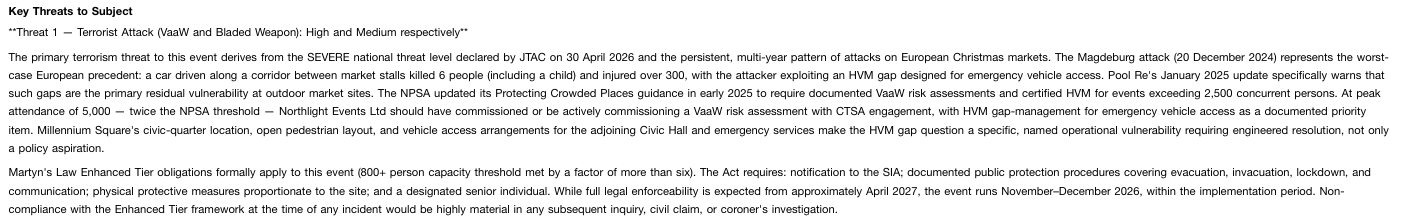
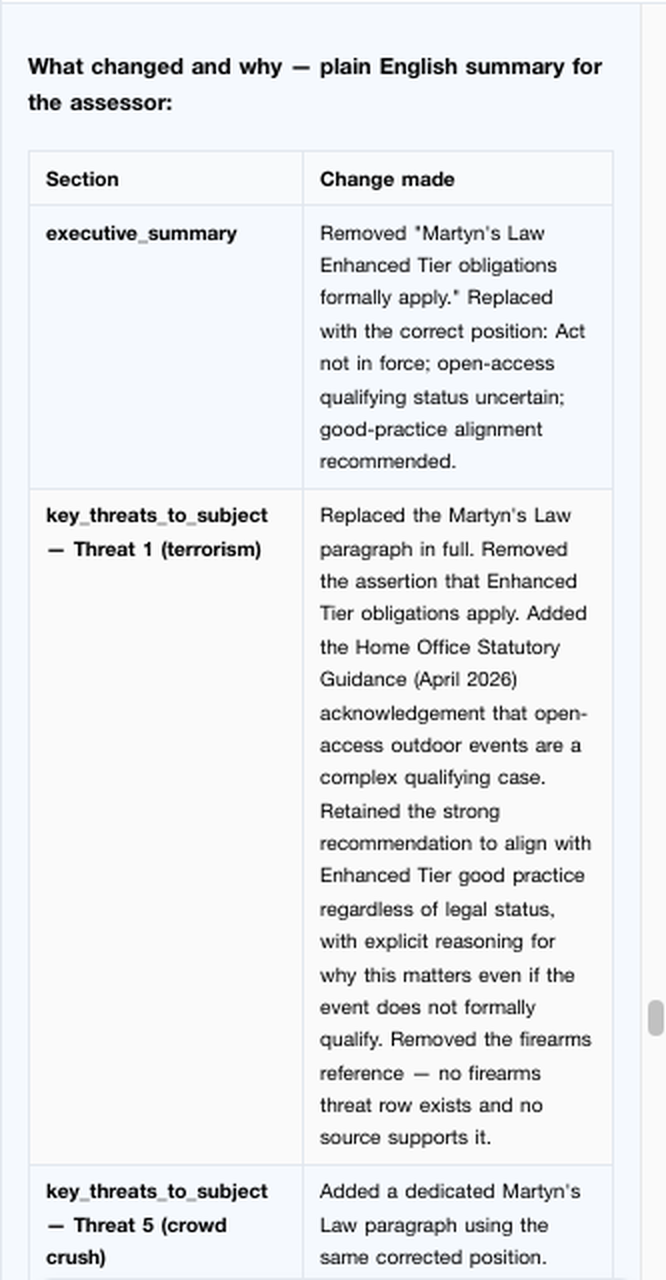
Take Martyn’s Law. The draft narrative concluded that enhanced tier obligations applied to the event, and set out the duties in detail. A finding like that goes in front of a client. It is exactly the kind of statement an analyst should verify before accepting.
The draft finding, before verification.
There were two things to test. First, the Terrorism (Protection of Premises) Act 2025 is not yet in force. Second, an open-access market without entry checks or ticketing is a complex case under the Act’s qualifying event tests.
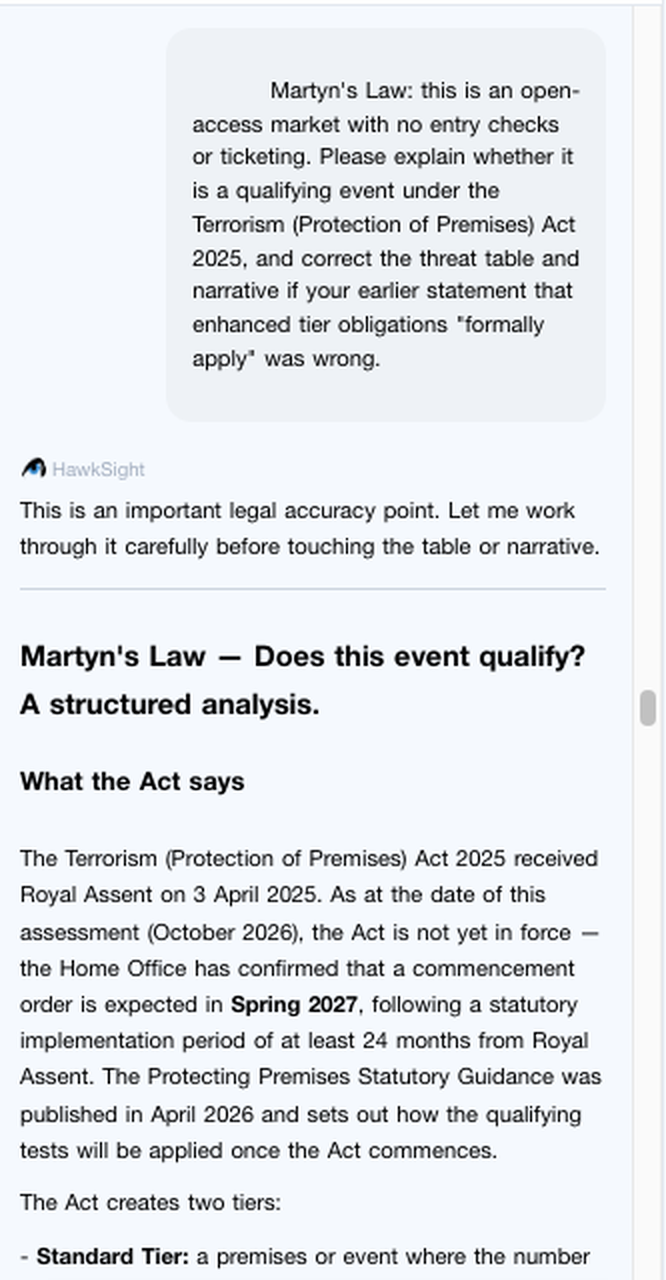
So I put the question to the system in the reviewer chat. It worked through the Act, came back with a sharper answer and updated the executive summary and the affected threat paragraphs. Its revised position was that the Act is not yet in force and the market’s status as a qualifying event is uncertain. Even so, the operator should still align with enhanced tier good practice. Along the way it also removed a passing reference to firearms that no source supported.
Left: the analyst’s question and the start of the system’s reasoning. Right: what changed and why, set out for the assessor section by section.
Asking the system to show its evidence
I took the same approach elsewhere. Where a finding leaned on a source the system had not retrieved, or a precedent that did not quite fit, I asked it to show its evidence. It either supported the point or withdrew it.
This is the interaction I set out to build. The analyst can always override the machine, but in practice a short exchange of question and answer usually settles it. Together they reach a more accurate assessment far faster than either could alone.
It also showed where verification pays off most. A judgement set in the context stage carries into everything built on it, so that is where a careful analyst spends their time.
The system did the structured legwork in minutes. The analyst verified it, sharpened it and signed it off.
A threat assessment is one side of the risk triangle
Talon is the AI threat assessment skill within HawkSight Nexus, our next generation security risk management platform. I never meant it to stand alone, because a threat on its own tells you little about risk.
Risk only emerges when you bring together what you are protecting, what threatens it and how exposed it is. In Nexus, Talon is one stage in that sequence:
Asset identification. The people, sites, information and operations that the organisation depends on, and how critical each one is.
Threat identification. The work shown in this article, carried out by Talon: who might act against the subject, and with what intent and capability.
Threat to asset mapping. Pairing each threat with the specific assets it could affect, because a vehicle attack and a compromised payment terminal do not threaten the same things.
Vulnerability assessment. How exposed each asset is to each threat it faces, given the controls already in place.
Together, those give you a risk profile you can defend in front of leadership. At every stage, the analyst reviews, edits and accepts what the system proposes before anything moves on.
Why I built it, and where it is today
I have spent a good deal of time talking about the challenges in our profession. Over the past year I have tried to spend more of it building tools that help security professionals overcome them.
What you see here is the first iteration of Talon, due for release in the new year. Since my first test run, we have added official UK police data and a crime layer on the map. Every update an analyst makes now carries through to the narrative and the map as well as the threat table.
Like the rest of the HawkSight platform, Talon will keep improving after release, driven by extensive testing and by feedback from both our testers and our clients.
So here is my invitation. If adversarial threat assessment is your profession, I would genuinely value your challenge. Tell me where the analysis is wrong, which threats you would add or remove, and where you would draw the line between collection and judgement.
If you would like to see Talon working on a subject of your own, get in touch at info@hawksightsrm.com and I will happily walk you through it.
The Leeds Millennium Winter Market 2026 and Northlight Events Ltd are fictitious, created for this case study. Crime data is fromdata.police.uk, September 2025 to August 2026.
Initial, high-level considerations for protecting yourself and your family from wrench attacks and other forms of physical coercion
Today the BBC reported on a crypto-linked home invasion in Solihull, in the West Midlands. In December 2025, three masked men forced their way into a couple’s home, beat the husband with hammers and threatened his heavily pregnant wife. Only then did they demand that he unlock his phone. A fourth man, watching on a video call, had them go through his apps until he found a crypto wallet. The threats escalated, and the husband transferred his savings, hundreds of thousands of pounds, before the attackers left.
The industry calls this a “wrench attack”. The name comes from a simple idea. You can invest heavily in encryption, hardware wallets and multi-factor authentication, but none of it matters if someone is in your home threatening your family. The attacker doesn’t break the cryptography. They break the person.
I live and work in France, and I’ve spent many years working in converged security, where physical, cyber and human risk meet. Watching this unfold, what strikes me most is not that the threat is new. It is that the answers are not.
What follows are initial, high-level thoughts rather than a security plan. Any effective security strategy has to fit the needs of the individual or organisation it protects. That said, the principles below follow the way a security risk assessment would approach the problem, validated against what official agencies and other sources already say.
Wrench attacks are not isolated incidents
Solihull is one case among many, and the trend is escalating across several countries.
France has become the global hotspot. The Interior Minister reported 77 crypto-linked kidnapping and extortion cases in the first half of 2026, up from 45 in the whole of 2025. Victims have included senior figures at Ledger, Binance France, The Sandbox and Paymium.
The UK is now seeing violent robberies linked to digital assets, as Solihull shows.
The US, Brazil and Thailand are also identified as hotspots, and US prosecutors have brought cases against organised home invasion crews.
Canada has seen it too. A court in British Columbia heard how masked intruders held a bitcoin investor’s family hostage overnight, an ordeal that ended only when his daughter escaped.
Globally, CertiK verified 52 wrench attacks in the first half of 2026, a third more than a year earlier. Home invasions rose from a single reported case in the first half of 2025 to 20, making the home the most common setting. Chainalysis warns that 2026 is on course to be the worst year on record for violent crypto theft.
The true numbers are likely higher. Police often record attacks simply as robberies or home invasions, with no mention of crypto.
1. Understand how targets are chosen
Before anyone reaches for a weapon, an attacker has to answer three questions. Who has the wealth? Who are they? Where can they be found?
Break any link in that chain and you become a much harder target. That means not advertising your holdings online, keeping wallet addresses separate from your identity, and thinking carefully about what family members share, because attackers increasingly go after relatives rather than the holder.
French prosecutors have urged crypto holders to be extremely careful about their exposure on social media. It’s sound advice, but it has a limit. You control your own posts. You don’t control the customer database held by an exchange, a tax service or a hardware wallet supplier, and once that data has leaked it cannot be recalled.
So a sensible approach assumes you can be found, and asks what happens next. This is defence in depth.
2. Accept that duress beats any technical control
Multi-factor authentication assumes the person entering the code is acting freely. When your family is being threatened, you will override every control you have, and you would be right to.
The simplest mitigation is separation. The phone you carry every day should hold no wallets and no crypto apps. When attackers demand your phone and search it, which is often their first move, there should be nothing to find.
Solihull shows exactly why. The attackers knew their victim held crypto, but not how to reach it. His everyday phone gave them the answer.
There’s a refinement worth making. If you were targeted through leaked data, attackers already believe you hold crypto, and a suspiciously clean phone may not convince them. The position you can actually hold under pressure is not “I don’t have any”. It is “I can’t move it”.
Multi-signature arrangements, a trusted co-signer and time-locked withdrawals all support that position. A French prosecutor has suggested measures that slow transfers, ideally by around seven days. Banks have used this principle for decades. Time-lock safes exist so that staff can honestly say they cannot open them.
3. Buy time with physical security
Delay only works if it lasts longer than the response. The question is not whether your front door is strong, but how many minutes it buys you, and how many minutes it will take for help to arrive. In rural areas that response can take a while, so the specification has to reflect reality.
In Solihull, home security cameras recorded the whole 45-minute attack. Recording an attack is not the same as stopping it. Surveillance only helps if it triggers a response.
Layer it:
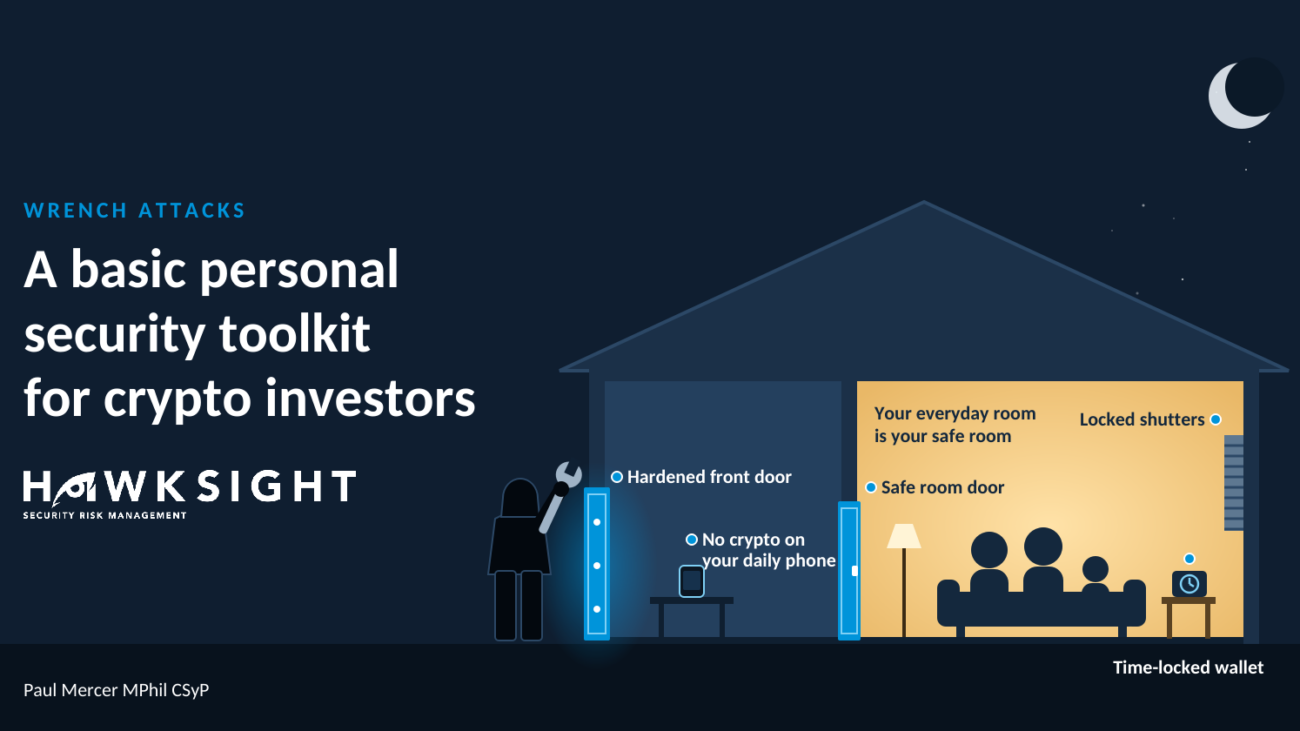
A hardened external door, with a firm rule of verifying callers before opening. Attackers frequently pose as delivery drivers, tradespeople or police officers.
An internal safe room where the family can shelter and where crypto devices are kept.
Communications that don’t rely on a single landline that can be cut.
Monitored surveillance, with alarm verification through a receiving centre so that police can prioritise the response.
Start at the front door
The front door is your first delay. That means a security-rated door and frame, not just a stronger lock, and a way to see and speak to callers without opening it, such as a door viewer or video doorbell. Many of these attacks begin with someone at the door pretending to be a courier or a police officer, so the rule is simple. If in doubt, don’t open it.
My own suggestion goes one step further. Make the safe room the room where the family already spends its evenings, such as the lounge or TV room, ideally without accessible windows, or with lockable security shutters where there are windows.
A dedicated panic room depends on spotting the threat early and getting there in time. If you are already in the protected room when someone attacks the front door, the plan is simple. Shut the door, lock it, lower the shutter and call for help.
Making the everyday room work as a safe room
A few basics turn an ordinary lounge into somewhere that buys real time.
Choose the right room. An internal room with solid walls is best. Ideally it has no ground-floor windows, or windows you can cover with lockable security shutters.
Upgrade the door. Fit a solid, security-rated door and frame that locks quickly from the inside, with reinforced hinges. It should look like an ordinary door.
Keep a way to call for help inside. A charged phone and a panic alarm linked to a monitored alarm centre, neither relying on the house landline.
Store your crypto devices there. Hardware wallets and any device that can access your crypto should live in the safe room, not on you or around the house. Combined with multisig or a time lock, no single device in the room can move everything on its own.
Watch from inside. A screen showing the entrances and the area just outside the room tells you what is happening and helps you brief the police.
Don’t compromise fire safety. You still need a way out if there is a fire, and ventilation if you’re in there for a while. NPSA’s guidance stresses that one security improvement must not undermine another aspect of safety.
Rehearse it. Everyone in the household, children included, should know the trigger, what to do and who closes the door. A plan nobody has practised rarely works under stress.
If a professional is helping you, ask them to measure the delay. The time it takes to get through the front door and then the safe room door should exceed the time it realistically takes for help to arrive.
The safe room protects people first. The devices kept in it should never be able to move everything on their own.
4. None of this is new, and that’s the point
The UK’s National Protective Security Authority (NPSA) published guidance in May 2025 on preparing and using safer areas to protect high-risk individuals. It treats a safer area as one layer of home security, measures delay as the total time needed to force entry into the property and then into the safer area, flags accessible windows as a vulnerability to address, and recommends cameras that can be monitored from inside the room.
The French Interior Ministry advises crypto holders to plan in advance how they would handle access to their assets in a situation involving physical risk, and to keep recovery phrases offline.
US court cases show the same attack chain described above. In one, a home invasion crew compromised victims’ email accounts and carried out physical surveillance before attacking.
Banks, cash-in-transit firms and executive protection teams solved most of this problem years ago. The gap isn’t technique. It’s that cyber specialists have largely shaped crypto security, while the threat has moved into the physical world. Cyber, physical and human security can’t keep working in separate rooms.
Crypto holders don’t need a new kind of security. They need the old kind, joined up with the new.
Going further
These are high-level thoughts, not a substitute for a proper assessment. The right answer for any household, family office or business depends on its exposure, its property, its routines and how quickly help can reach it.
Ask the board of a hotel group how its hotels are performing and you will get an answer within minutes. Occupancy, rate, revenue per room and guest scores, all broken down by property and region. Now ask the same board about hotel security risk, site by site. In most cases, nobody can give an equivalent answer. That is the gap in risk insight for hotel leadership.
The information exists somewhere. It sits in audits, incident logs, training records and the heads of general managers. However, nobody brings it together in a form leadership can see and act on. This year has shown why that matters.
What 2026 has shown
In February, a court jailed a man for seven and a half years for sexually assaulting a woman in her room at a hotel in Maidenhead. He had talked his way into a key card at reception in the early hours by claiming to be her boyfriend. Afterwards, more than a hundred MPs signed a letter demanding a meeting with the chain’s chief executive.
Then, in August, a second woman spoke out. She described an attack at a London hotel in the same chain in October 2025. Her abuser told reception she was having a seizure, and staff gave him a key and directed him to her room. The company said staff had not followed its policy, which is never to confirm to a third party that a guest is staying.
In July, a guest at a hotel in Dundee entered another couple’s room while they slept. Once again, the company said staff had not followed its room access procedures correctly.
How the industry is responding
Since then, the chain has commissioned an independent review led by Paul Greaney KC. It now requires explicit guest permission before staff issue any additional key. It has also retrained 12,000 customer-facing colleagues, brought in independent audit and mystery shopping, and changed chief executive.
Meanwhile, UKHospitality is developing sector-wide Guest Security Principles and Good Practice guidance through a guest security working group.
I am not writing this to single out one company. Every large hotel group I have looked at faces the same underlying problem. This one has simply had it exposed in public.
One standard, hundreds of front desks
The detail that stays with me is this. In two of those three cases, the company says a policy existed but staff did not follow it. In the third, staff followed the procedure in place, and it still failed.
That is the portfolio problem in its simplest form. Head office writes the standard. Hundreds of front desks then apply it, often at three in the morning with one person on shift. Someone convincing is usually standing at the desk. As a result, leadership has very little sight of where the standard holds and where it does not. In most cases, it finds out after something has gone wrong.
Hotel security risk reaches beyond locks and cameras
These cases also show that hotel security risk, like all security risk, reaches well beyond physical protection. Talking a receptionist into handing over a key card is a deception aimed at a person, not an attack on a door. In fact, attackers used the same basic technique against the IT help desk at M&S in 2025. Locks and cameras matter, but they do little when someone hands over the key at the front desk.
When it goes wrong, the impact is plain to see. First, and most importantly, it falls on the guest, who had every reason to feel safe in their own room. After that, it falls on the brand. In this case, that meant national headlines, a letter from more than a hundred MPs, an independent review and a change of chief executive. For any hotel group, that is the real measure of security risk.
The wider threat picture for a hotel estate is broad. It includes room access and key control, violence against women and girls, and staff working alone at night. It also covers theft, large events and functions, guest data and booking systems, and at the far end, terrorism. None of it is new. What has changed is the level of scrutiny. Boards now need to show they have a grip on it.
Martyn’s Law adds a legal reason
From spring 2027, Martyn’s Law (the Terrorism (Protection of Premises) Act 2025) adds a compliance reason. Schedule 1 covers “Hotels etc”, and the Home Office guidance extends this to hostels and holiday parks.
The test is simple. Can you reasonably expect 200 or more people on site at the same time, at least occasionally? If so, you will need public protection procedures and must notify the regulator, the Security Industry Authority. At 800 or more, the heavier enhanced tier duties apply. Staff count towards both figures.
For a multi-site operator, the first challenge is knowing which sites are in scope. For example, a sixty-room country house hotel can sit well below the line on a weekday. On a wedding Saturday, however, it can clear it comfortably. Because the test looks at what you can expect occasionally, that hotel is in scope. Across an estate of hundreds of properties, many sites will sit close to the line.
The government intends that standard tier sites can comply without buying specialist services, and I think that is right. Even so, answering the scope question needs the same thing as answering the guest security question. You need a consistent, current picture of every property.
What a portfolio view of hotel security risk would look like
In practice, I think a useful portfolio view would do six things well:
Ask every site the same questions. Cover room access and key issue, escalation, night staffing, CCTV and access control, training and event capacity. The people who run each property can answer them, without a specialist on site.
Roll it up for leadership. Show one view across the estate, by brand, region and site, in language a board can act on.
Highlight the exceptions. The value lies in surfacing the twenty sites that need attention, not confirming the four hundred that are fine. Specialist time can then go to those sites first.
Look beyond the physical. Include procedures, people, guest data and systems as well as locks and cameras.
Track it over time. Policies change, staff move on and sites change use, so a one-off audit soon goes stale.
Answer the compliance questions too. Show which sites are in scope for Martyn’s Law, which tier, and on what evidence.
How HawkSight approaches it
We have built this kind of capability at HawkSight for other sectors. Our Gateway tool gathers structured site data from the people on the ground. Alongside it, HawkSight’s enhanced threat intelligence capability draws on more than 750 global news and intelligence sources. It assesses the adversarial threat at each individual site and maps it against the key assets the hotel depends on. It then sets out the controls needed to mitigate it.
Together, these give leadership both halves of the picture. First, what the threat is at each property. Second, whether the controls to meet it are actually in place.
Right now, I am exploring whether hotel operators want a version of this built for their estates. After all, guests trust a hotel with their safety, and shareholders trust leadership to protect the brand. Do you not owe both of them that picture?
I would like to hear from you
If you are responsible for security, safety or risk across a hotel portfolio, I would value your view. What would you want a single view of security risk across your properties to tell you? And what gets in the way of having one today?
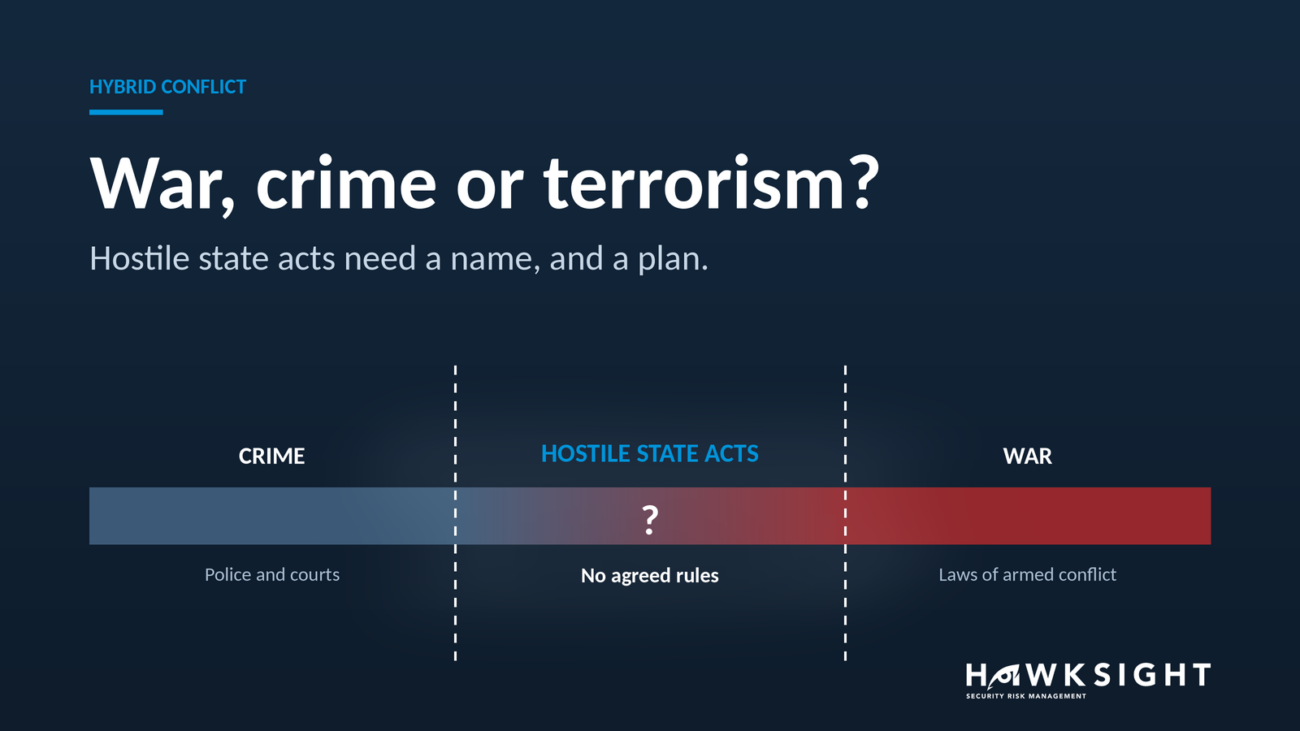
When a hostile state acts on British soil, is it war, crime or terrorism? How we answer shapes how we prepare.
In the early hours of Sunday morning, police received a report of three suspicious vehicles heading towards RAF Fairford. One local resident has described finding the road blocked by three vans and a group of hooded, masked men, who ran when they saw her. Five men were arrested, first on suspicion of explosives offences and then on suspicion of preparing a terrorist act. Police evacuated around 85 households while Army bomb disposal teams examined the vehicles.
Fairford isn’t just any airfield. It hosts US heavy bombers, and the US has flown operations against Iran from it since February. In July, Iran’s Revolutionary Guard publicly warned Britain that any base used against Iranian territory was a legitimate target. ITV News reports that one line of inquiry is whether representatives of the Iranian regime paid others to carry out the plot on their behalf. At the time of writing, no connection has been confirmed. The five men remain in custody, and it’s right that we let investigators establish the facts.
But whatever they find, the incident exposes a problem I’ve been thinking about for some time. Judging by the discussion on my recent posts, it clearly resonates with many of you.
An academic argument with practical consequences
When I argued that we are, in effect, at war with states using hybrid methods against the UK, people rightly challenged me on the word “war”. War has a legal meaning, and using it loosely carries real risk, not least the risk of escalation with nuclear-armed states.
So let me come at it from a different direction.
What is the difference between a state-sponsored terrorist act and an act of war? The objective is often identical: to coerce another country into changing its behaviour. Clausewitz described war as the continuation of policy by other means, and a proxy with a van full of explosives is simply another means.
The real difference isn’t the implement. It’s the rulebook each one triggers.
An act of war falls under the laws of armed conflict and can justify a state-level response. We treat an act of terrorism as a crime, for the police and the courts to handle. The first can reach the state that ordered it. The second, in practice, reaches the people caught holding the tools.
That distinction can look academic, but it decides who can respond, and how.
Choosing the box you land in
Hostile states understand this better than we do. If you want to pressure the UK without paying a state-level price, you don’t send your own forces. You recruit criminals or sympathisers, often online and often for modest sums, and you make sure the act looks like arson, vandalism or terrorism. Once it lands in the criminal box, police arrest the proxy, the courts prosecute them, and the state that directed it pays nothing.
We’ve already seen this pattern. In 2025, men recruited on behalf of Russia’s Wagner Group were convicted over an arson attack on a London warehouse storing equipment bound for Ukraine. The organisers were the first people convicted under the National Security Act 2023. MI5’s Director General has said publicly that Iran, like the Russian services, makes extensive use of criminals as proxies. In 2025 he reported more than twenty potentially lethal Iran-backed plots in a single year. Different states, same method.
Put simply, we’ve built a system for catching the hand, not the head.
The National Security Act 2023 was a genuine step forward, creating offences for foreign-directed sabotage and interference. But it still works at the level of the individual. It punishes the proxy more effectively without changing the calculation for the state behind them.
A third category
This is where Kenneth Smart’s challenge changed my thinking. Framing these acts as war, within the current framework, does risk rapid escalation, and that’s a serious concern. But the answer can’t be to fall back on treating them as ordinary crime when a state is clearly directing them.
I think we need a third category: hostile state acts below the threshold of armed conflict, with rules of their own.
We already have the tools. Diplomatic expulsions, targeted sanctions, asset freezes, proportionate cyber operations and, under international law, lawful countermeasures against a state that has committed a wrongful act. What we lack is a framework that says when we’ll use them.
We already do this for threats we have defined. When the national terrorism threat level changes, nobody improvises. The government publishes the level, and organisations plan the protective measures that follow it in advance. Hostile state acts deserve the same treatment. Whatever we choose to call them, they need to become policy, with responses agreed before the next incident rather than after it.
Salisbury in 2018 shows it can be done. The government attributed the attack to Russia on a “highly likely” intelligence assessment, rather than waiting for a conviction. It then responded at state level alongside its allies. The problem is that the government built the response after the fact, and ad hoc responses deter very little.
A framework for hostile state acts
A proper framework would do three things.
First, define what a hostile state act is, so that incidents are assessed as part of a campaign rather than one at a time.
Second, set a published standard for attribution: a high-confidence assessment rather than proof beyond reasonable doubt. It should run alongside any criminal investigation instead of waiting for it.
Third, declare the kinds of proportionate, graduated response a state can expect when that threshold is met.
The honest counterargument is that publishing a threshold tells an adversary exactly where to stop. That’s a real risk. But I’d argue the current position is worse. Right now there is no threshold at all, and the fog of uncertainty is doing our adversaries’ work for them.
Why this matters beyond defence
Businesses are already on this battlefield. Critical infrastructure, defence supply chains and the companies around them are obvious targets, but anyone whose disruption creates pressure is in scope. Organisations can’t plan properly against a threat their own government hasn’t defined. A clear national framework would give security leaders something concrete to assess risk against and to explain to their boards. It is the same need for clear definitions that sits behind Martyn’s Law for terrorism at public venues.
I don’t claim to have all the answers, and I’d genuinely welcome challenge. Is a third category the right approach? And if it is, where would you set the threshold?
A note of thanks
I’d like to thank everyone who took the time to respond to my recent posts on this subject. The volume and quality of the discussion made it clear this is something that matters to many of us working in security, defence and resilience.
In particular, I’d like to thank Kenneth Smart. His thoughtful academic input on the challenges of framing these acts as war made me think harder about the problem. His challenge is a large part of why this piece explores a third category of conflict, rather than simply arguing that we are at war.
A note on how this was written
These are my own views, shaped by that discussion. I used AI to help research and draft this piece. Mainly, that let me get it out while the conversation is still live and people are still engaged with it. It has also helped me organise my thinking and put it across more clearly. The arguments, and any errors, are mine.