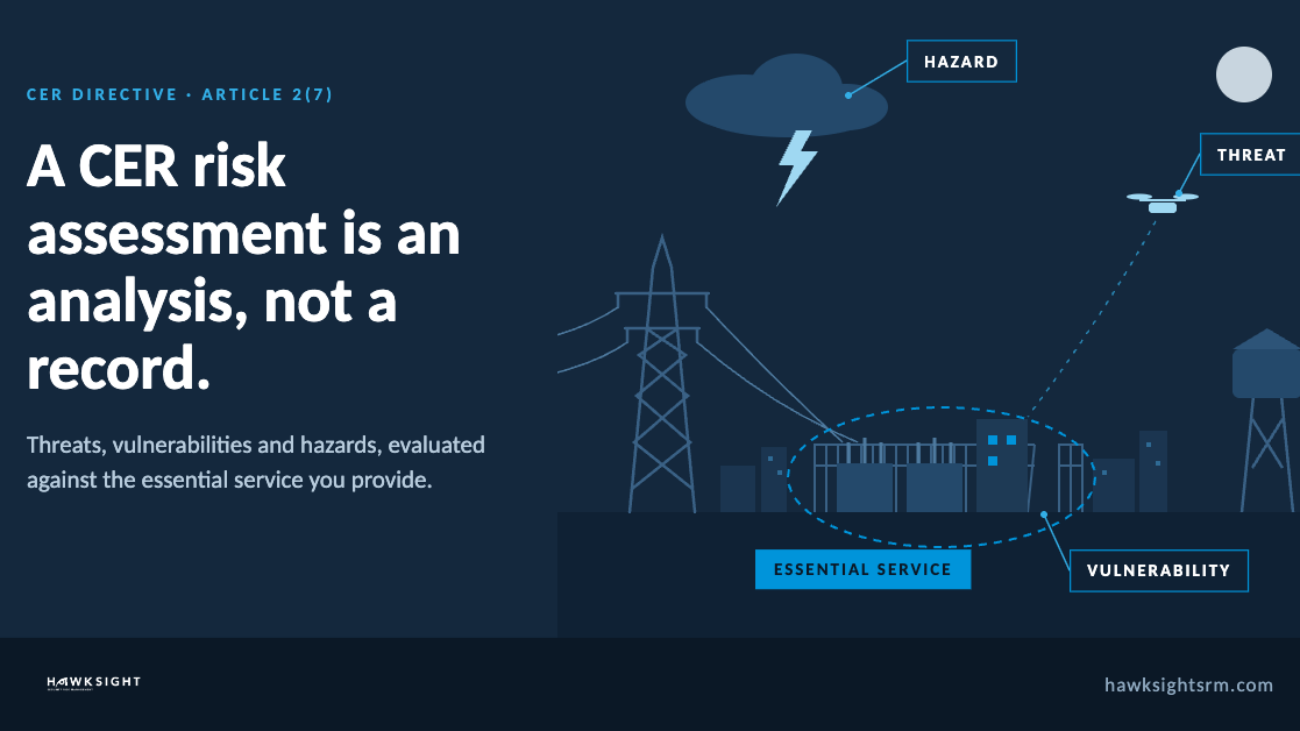
Under the CER Directive, a risk assessment is not a record of what you already have. It is an analysis of what could go wrong, why, and what it would do to your essential service.
Over the summer, competent authorities across the EU have been identifying the organisations they consider critical entities. For those organisations a clock is now running, and the first thing it counts down to is a risk assessment.
Most will produce one on time. The more useful question is whether it will meet the definition the Directive actually uses. That definition is more demanding than many people assume.
What CER is, and who it reaches
Directive (EU) 2022/2557, CER for short, obliges designated organisations to be resilient against all hazards. Not just cyber. Not just natural disasters. All of them.
The Directive defines resilience broadly. It means being able to prevent, protect against, respond to, resist, absorb and recover from incidents that disrupt an essential service.
It covers 11 sectors: energy, transport, banking, financial market infrastructure, health, drinking water, waste water, food, digital infrastructure, public administration and space.
Organisations do not designate themselves. The national competent authority does it, based on three tests. The entity provides an essential service. It operates critical infrastructure in that Member State. And an incident would cause significant disruption.
Two points are worth getting right early. Article 8 identifies entities in banking, financial market infrastructure and digital infrastructure but exempts them from the substantive duties. Their resilience obligations sit mainly under DORA and NIS2. And CER does not apply in the UK, but it still reaches UK organisations through the EU operations they run, or as suppliers to EU critical entities.
When the risk assessment is due
The most common misreading I see is that the risk assessment was due on 17 July 2026. It was not. That was the date by which Member States had to identify their critical entities (Article 6(1)).
The authority then notifies each entity within a month, and the entity’s own clock starts on that date. From there:
| Duty | Due | Article |
|---|---|---|
| Risk assessment | Within 9 months of notification | 12(1) |
| Resilience measures, resilience plan, liaison officer | From 10 months after notification | 6(3), 13 |
| Incident notification (initial report within 24 hours) | From 10 months after notification | 6(3), 15 |
| Review of the risk assessment | Whenever necessary, and at least every 4 years | 12(1) |
Take an entity notified on the last possible date, 17 August 2026. Its risk assessment would be due by 17 May 2027, with resilience measures in place from 17 June 2027. Earlier notification brings both dates forward. National transposition laws can also vary the mechanics, so check the law in each Member State where you operate.
Notice how little time separates the two. Article 13(1) requires the resilience measures to rest on the risk assessment. So the assessment is not a box ticked in May. It is the foundation everything due in June is built on.
What the law means by a risk assessment
CER is precise about this. Article 2(7) defines a risk assessment as:
“the overall process for determining the nature and extent of a risk by identifying and analysing potential relevant threats, vulnerabilities and hazards which could lead to an incident and by evaluating the potential loss or disruption of the provision of an essential service caused by that incident”
Read it slowly and three things stand out. You must identify and analyse threats, vulnerabilities and hazards, not simply list them. You evaluate impact against one yardstick, the essential service. And the Directive defines risk as the magnitude of the loss or disruption combined with the likelihood of the incident.
Article 12 then sets out what the assessment must take into account:
- Inputs: the Member State risk assessment and other relevant sources of information.
- Scope: all relevant natural and man-made risks, including cross-sectoral and cross-border risks, accidents, natural disasters, public health emergencies, and hybrid threats and other antagonistic threats, including terrorist offences.
- Outward dependencies: how far other sectors depend on the essential service you provide.
- Inward dependencies: how far you depend on essential services from other sectors, including in neighbouring Member States and third countries.
It is worth being careful with language here. The articles name hybrid and antagonistic threats, including terrorism. Sabotage appears only in the recitals, and the word insider does not appear in the risk assessment articles at all. Insider risk enters through the employee security measures in Article 13(1)(e) and the background checks in Article 14. That is why a good assessment treats people as part of the threat and vulnerability picture, not as a separate HR matter.
Where assessments are likely to fall short
The good news is that existing work counts. Article 12(2) lets you reuse risk assessments and documents produced under other legal obligations. The competent authority may also declare an existing assessment compliant, in whole or in part.
That reuse carries a trap, though. Many organisations hold excellent business continuity plans, hazard registers, incident logs and control inventories. Those documents tend to be strong on natural hazards, accidents and dependencies. They are often much weaker on the two things the definition names first: threats and vulnerabilities.
An incident log tells you what has happened. It tells you very little about a capable, motivated adversary who has not yet acted. Nor does it reveal a hybrid campaign that blends cyber, physical and human activity. A control inventory tells you what exists. It does not tell you whether those controls would hold against the threats your site actually faces.
So the risk is not that organisations produce nothing. It is that they compile records and call the result a risk assessment. Then they build a resilience plan on a picture that never analysed the threat at all.
What a compliant method looks like
If you build the method from the definition outwards, the shape of a compliant assessment becomes fairly clear. In our own work we follow this sequence. It maps directly onto what Articles 2, 12 and 13 ask for.
First, build the picture
- Start with the essential service. Define what the entity delivers and the sites, systems, processes and people behind it. Set out what loss or disruption would actually look like. Map dependencies in both directions, including cross-border and third-country suppliers.
- Assess the threat. Use the Member State risk assessment as a formal input. Then add current intelligence: location-based crime data, open source reporting and the wider geopolitical and hybrid picture. For antagonistic threats, ask who could act against this specific service, and with what intent and capability. Assess natural hazards and accidents alongside them, on the same basis.
- Test vulnerabilities against those threats. Physical, cyber and people vulnerabilities belong in one converged view, because that is how a capable adversary will look at you. The question is not whether a control exists. It is whether the control would stop the threats you have just identified, including where contractors’ staff have access.
Then evaluate, trace and review
- Evaluate the risk against the service. Score likelihood and the magnitude of disruption on a consistent, ISO 31000-aligned scale. That lets you compare and prioritise sites and assets across a whole portfolio.
- Trace every measure back to a risk. Link each resilience measure to a specific risk and to one of the six Article 13 areas: prevent, protect, respond, recover, employee security and awareness. That trail turns a resilience plan into evidence.
- Define your review triggers. At least every four years is the minimum. Set out what else counts as “whenever necessary”: a change in the threat picture, a change to the estate, an incident, or a revised Member State assessment.
- Make it readable at board level. CER places accountability on the entity. Show leadership where the exposure sits and why the measures are proportionate, in language they can act on.
Where technology fits
Technology helps a great deal with threat, vulnerability and risk evaluation, particularly across large portfolios. AI can take on much of the heavy lifting in gathering and structuring threat data. But judging what a threat means for a specific essential service still needs an experienced security professional. The law asks for analysis, and analysis is a human responsibility.
If you supply critical entities
CER places no direct duties on suppliers, but that does not mean suppliers are untouched. Critical entities must assess how far they depend on others (Article 12(2)), plan for alternative supply chains (Article 13(1)(d)), and manage the security of external service providers’ personnel (Article 13(1)(e)).
In practice, security providers, facilities contractors and specialist suppliers should expect questions. Clients will ask about continuity, access control, vetting and exercising, and add contract terms that pass those requirements down. You may not be designated, but you will very likely be asked for evidence.
The real test
The test of a CER risk assessment is not whether it exists by the deadline. It is whether you can trace every measure in your resilience plan back to a threat, a vulnerability or a hazard you actually analysed.
If your competent authority asked you tomorrow to show that trail, could you?
Source: Directive (EU) 2022/2557 on the resilience of critical entities, EUR-Lex. Article references are to the Directive; national transposition laws may vary the detail.